






What is post-quantum cryptography?
Why quantum computers threaten the signatures most coins use, what ML-DSA is, how Quantus handles its larger signatures, and why mining stays the same.
Why are quantum computers a threat to coins?
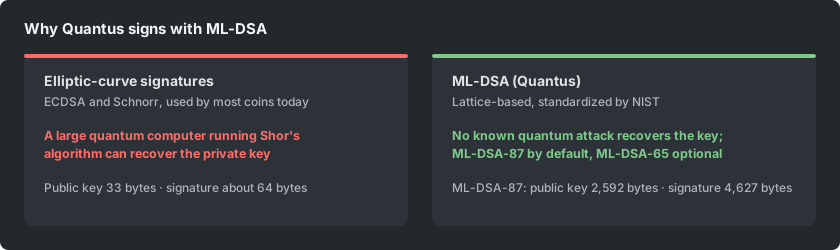
Most cryptocurrencies sign transactions with elliptic-curve schemes such as ECDSA or Schnorr. A signature proves the owner of a key approved the transaction.
These schemes rest on a maths problem that ordinary computers cannot solve in any practical time. A large enough quantum computer running Shor's algorithm could solve it.
Anyone with such a machine could work out a private key from its public key. Then they could spend the coins.
What is ML-DSA?
ML-DSA is a digital signature scheme built on lattice problems. No efficient quantum attack on them is known.
It was standardized through the NIST post-quantum cryptography program. It grew out of the CRYSTALS-Dilithium design.
Quantus signs every transaction with it:
- ML-DSA-87 by default.
- ML-DSA-65 for users who want smaller signatures.
What does it cost, and how does Quantus handle it?
Post-quantum signatures are much larger. An ML-DSA-87 signature is 4,627 bytes, where an elliptic-curve signature is about 64.
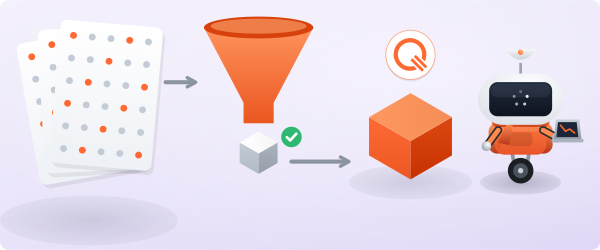
Quantus uses zero-knowledge proofs and cryptographic aggregation to reduce the extra space this takes on-chain.
Does it change mining?
No. Proof of Work relies on a hash function, not on signatures. Hash functions are far less exposed.
The best known quantum speedup against them, Grover's algorithm, is only quadratic. Quantus mines on the Poseidon2 hash.
For you as a miner nothing changes. You mine with your qz address like any other coin.